
Every always-on admin account is an attack vector. Every 'just in case' permission is blast radius you didn't need. Multiplier gives you complete visibility into who has access to what—plus just-in-time provisioning and time-bound access that eliminates standing privileges entirely.
Try for free
 ITHELP-8424:10 PM
That temporary admin access for the deployment? It should be temporary. Multiplier lets you grant time-bound access that automatically revokes itself. No more 'I forgot to remove it.' No more standing privileges that outlive their purpose. Set the expiration, and it's handled.
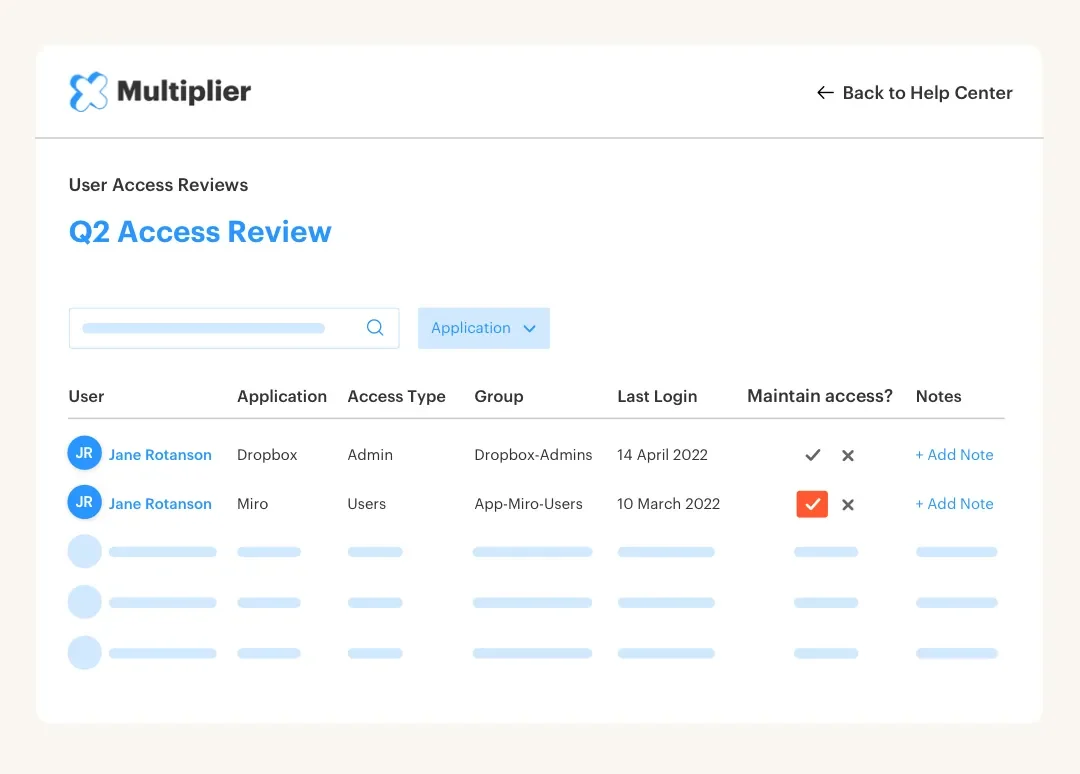
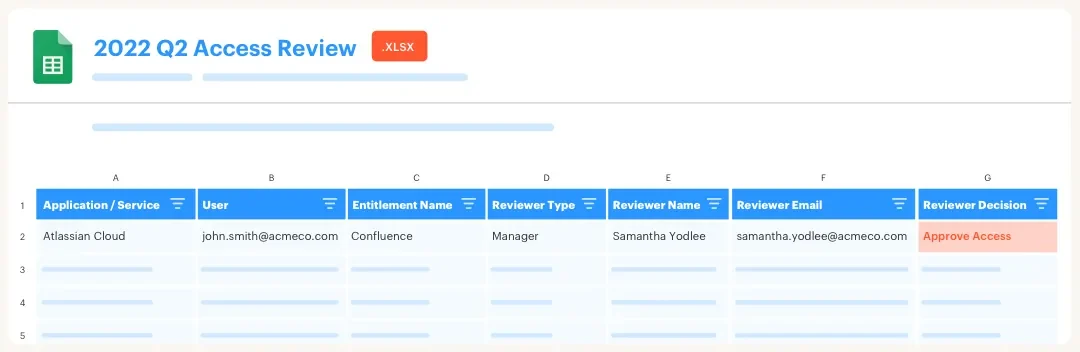
Why grant standing access 'just in case'? With just-in-time provisioning, users request access when they actually need it. Approve in seconds. Access activates instantly. And when the job's done, it disappears. Zero standing privileges means zero standing risk.
Everyone agrees with least privilege in theory. In practice? People accumulate access like digital hoarders. Multiplier flags over-provisioned accounts, suggests appropriate access levels, and makes it easy to right-size permissions. Principle of least privilege, meet enforcement mechanism.
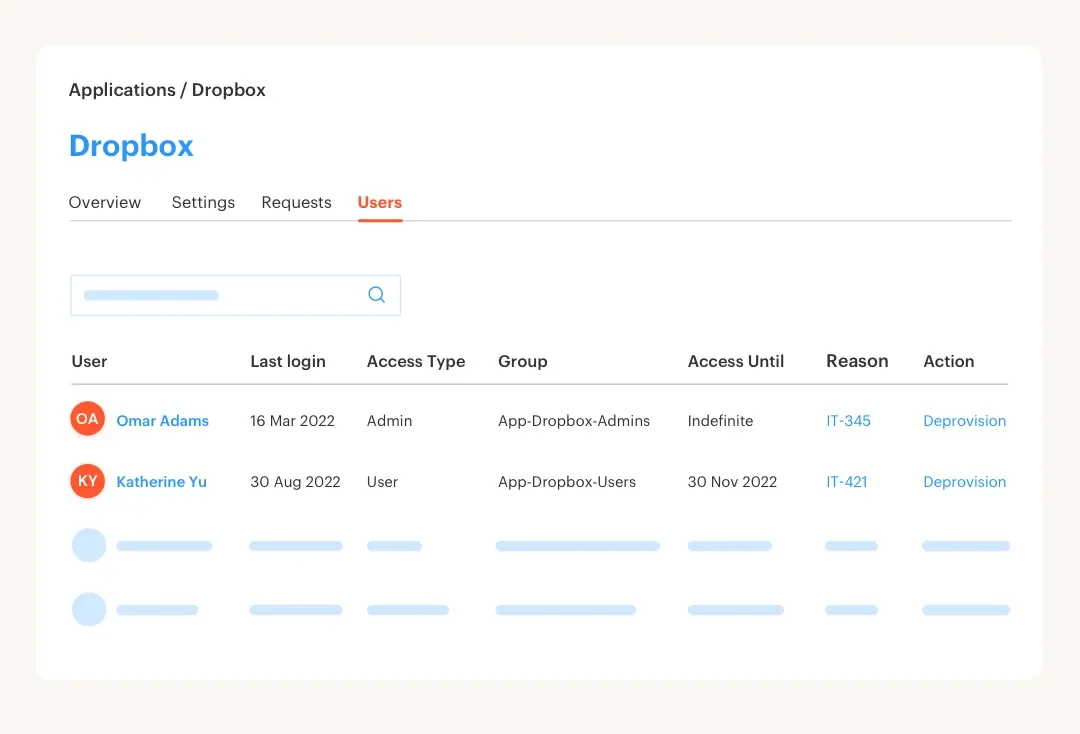
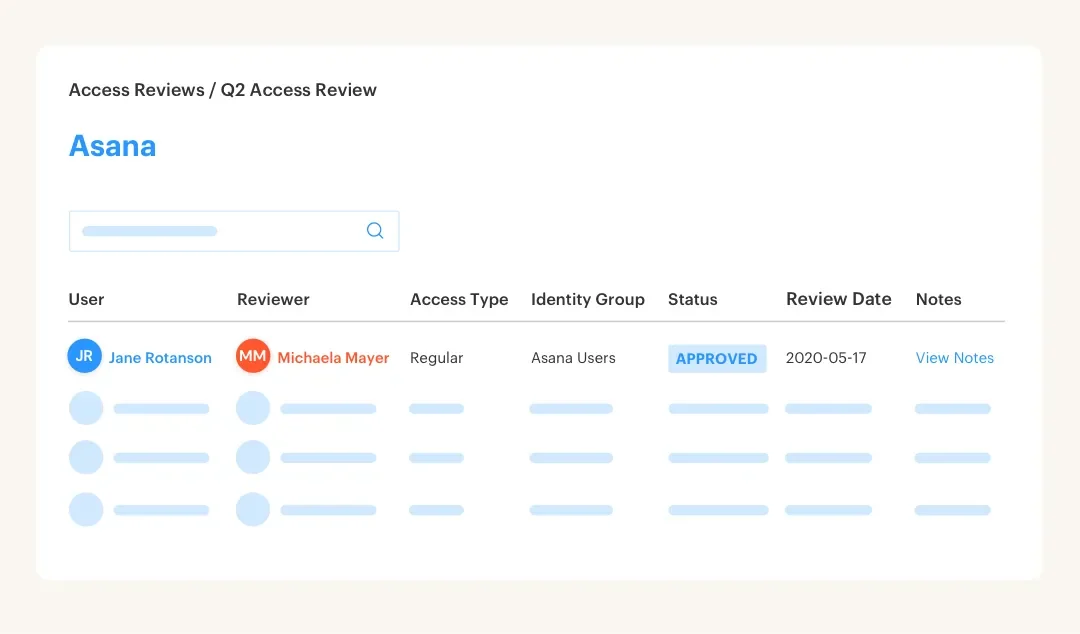
Ask yourself: who has access to your production database right now? If the answer takes more than 10 seconds, you have a visibility problem. Multiplier shows you exactly who has access to what, across every system, in real-time. No more spreadsheet archaeology.